Become a CISA (Certified Information Systems Auditor)
with AIA's Expert-Led Training.
CISA is the global standard certification for professionals who audit, control, and secure information systems. Awarded by ISACA and recognised in 180+ countries trusted by the world's leading organisations, CISA validates the expertise that modern IT audit and governance roles demand.
AIA designed the CISA Prep Course for working professionals who need structured, exam-aligned preparation. Guided by Puneet Garg, an APMG Authorised Trainer. This course combines recorded video lectures, expert-created short study materials, and the official ISACA study resource kit to fully prepare you.
(Structured learning)
(Mentor guided sessions)
(AIA + ISACA Study Resources)
(Condensed Short Notes)

Loading videos...
CISA Certification - Eligibility and Requirements
Understand the requirements and experience waivers available to fast-track your CISA credential.
Understand the requirements and experience waivers available to fast-track your CISA credential.
CISA Certification is the right path for those who:
- Have a minimum of 5 years of professional experience in information systems auditing, control, or security.
- Work in IT audit, IS governance, risk, compliance, or cybersecurity roles.
- Candidates with basic knowledge of IT Audit concepts are recommended to obtain the IT Audit Fundamentals certification to better understand the domain.
If you're still building your experience, you can begin preparing now and apply for certification once you meet the requirements.
Experience Waivers Available
ISACA allows substitution of up to 3 years of the required experience:
| Qualification / Background | Waiver Duration |
|---|---|
| Bachelor's Degree (any field) | 2 Years |
| Master's Degree (IT / Security related) | 3 Years |
| CIMA / ACCA (Full Certification) | 2 Years |
| IS or Financial Audit Work Experience | 1 Year |
Work Experience Requirements
ISACA requires a minimum of 5 years of professional work experience in information systems auditing, control, or security.
At least 1 of the 5 CISA domains must be covered in your experience.
Experience must be earned within 10 years before the certification application date.
Or within 5 years after passing the CISA exam.
Your Complete Guide to CISA Mastery -
Value, Learning, Format
Your Complete Guide to CISA Mastery -
Value, Learning, Format
VALUED FOR
- IT Auditors
- Cybersecurity Professionals
- Risk Professionals
- Compliance Professionals
- Governance & Control Professionals
- IT Consultants & Advisors
FORMAT OF EXAM
- Questions - 150 MCQs
- Duration - 4 Hours
- Passing Score - 450 / 800
- In Person & Online Based Exam
- No Negative Marking
DOMAINS FOR LEARNING
- IS Audit Standards & Ethics
- IT Governance Frameworks
- Information Systems Operations
- Business Resilience & Recovery
- Protection of Information Assets
- Exam Strategy & Approach
What Makes AIA's CISA Prep Stand Apart
AIA Short Notes & Exam Distractors

APMG Authorised Trainer
ISACA Accredited Training Partner

Official ISACA Study Resources

Instant Doubt-Solving Support
Trusted & Authorized by Leading Global Bodies
With globally recognized certifications, authorized partnerships, and a proven track record of success, we empower professionals and organizations with CISA training excellence.
With globally recognized certifications, authorized partnerships, and a proven track record of success, we empower professionals and organizations with CISA training excellence.
10,000+ Hours
Expert Mentoring Sessions
99.6%
Success Rate
2,000+ Professionals
Trained & Certified
40+ Countries
Served
Know Your Trainer
Not Just a Trainer, But Your Success Coach
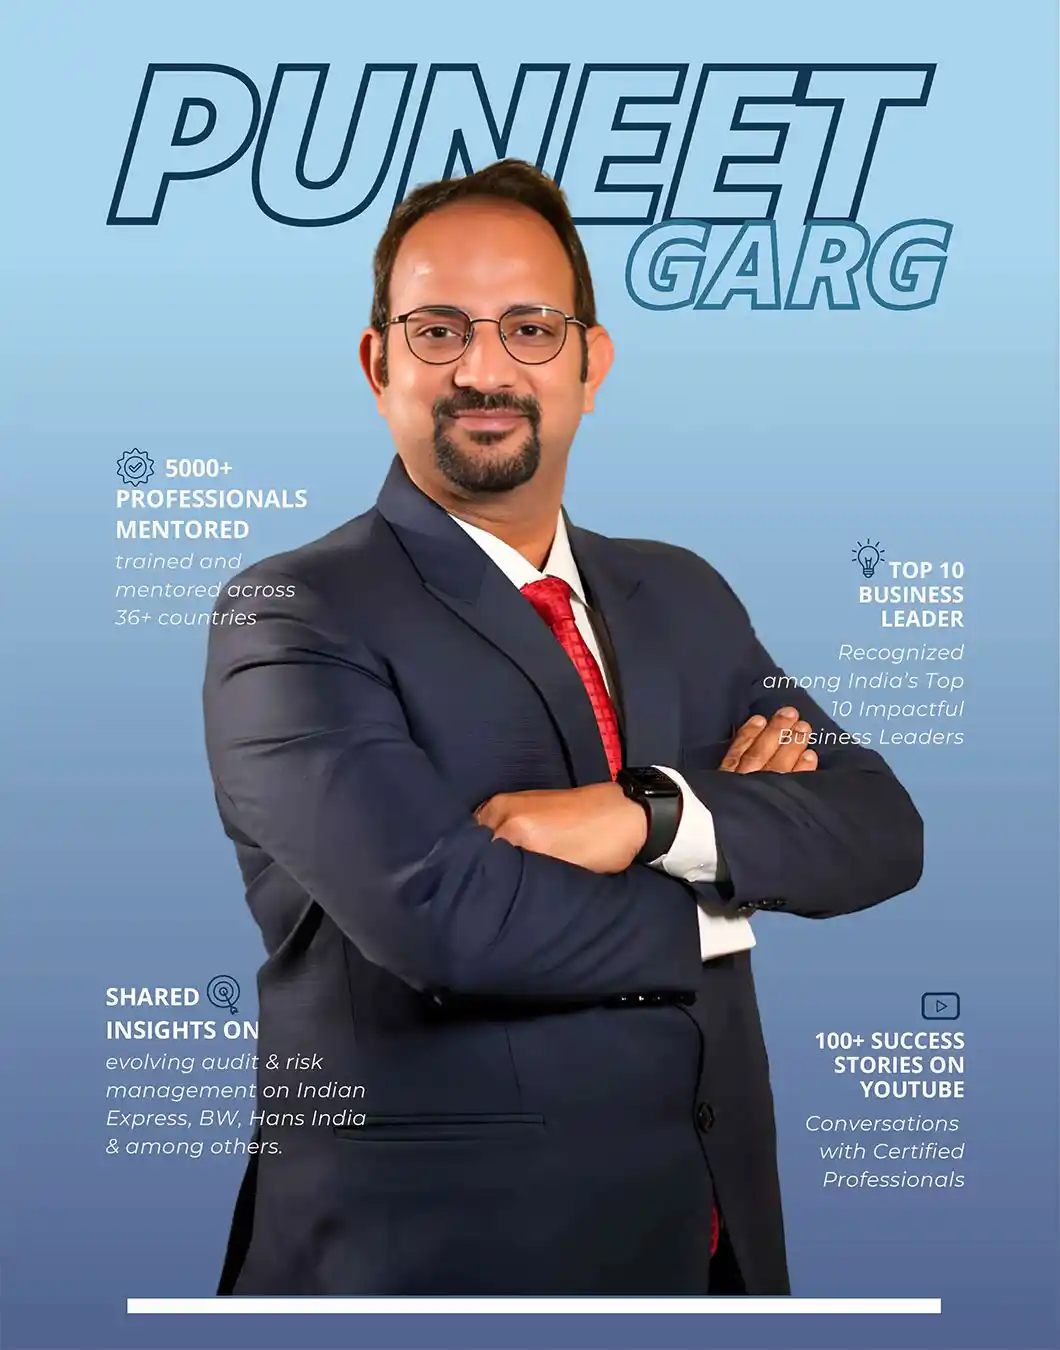
Puneet Garg is a globally certified audit leader with over 22 years of experience across internal audit, risk management, compliance, forensics, and finance . Holding prestigious credentials including CA, CS, CIA, CAMS, CISA, and CFE, he brings deep technical expertise and practical insight to his role as a mentor and industry expert.
Over the course of his career, he has worked with leading multinational organizations such as Samsung, Hyundai, Panasonic, and Alchemist and has served as the Head of Internal Audit at DCM Shriram Industries Ltd., where he led enterprise-wide audit, risk, and control initiatives. His strong foundation in corporate governance, internal controls, and fraud investigation has established him as a trusted authority within the audit and compliance ecosystem.
Driven by a genuine passion for teaching, he has mentored and trained 2,000+ aspirants, helping them build successful careers and confidently master complex certifications themselves first. At the Academy of Internal Audit (AIA), he is known for simplifying challenging concepts through real-world examples, practical case discussions, and engaging teaching methods that learners consistently value. In addition to individual mentoring, he has conducted specialized training programs for corporate teams, regulatory bodies, and investigative agencies.
He has also served as an authorized trainer with the NSE Academy, contributing to the professional development of finance and audit professionals across India.
He is now an authorized trainer with ISACA, further strengthening his contribution to the professional development of audit, risk, and information security professionals.
In recognition of his impact on ethical leadership and capability building in the profession, CEO Insights India featured him among the Top 10 Impactful Business Leaders in India.
CISA Certification Curriculum
At AIA, we design our CISA preparation programme to ensure that candidates develop both exam readiness and real-world audit judgement. The course structure helps learners understand IT governance frameworks, assess system vulnerabilities, evaluate business resilience, and apply audit standards the way they are tested and practised, in the field.
FOR MORE INFORMATION
What's Included in the AIA CISA Exclusive Study Resources
AIA provides comprehensive CISA exclusive study resources, combining structured learning materials, expert guidance, and exam practice resources.
AIA provides comprehensive CISA exclusive study resources, combining structured learning materials, expert guidance, and exam practice resources.
Short Study Notes
You get 200 pages of concise, exam-focused study notes curated by AIA’s expert faculty. These notes are designed with everything you need to crack the CISA exam. Hard books are delivered directly to your doorstep, so you can study comfortably offline as well.
LMS (Learning Management System)
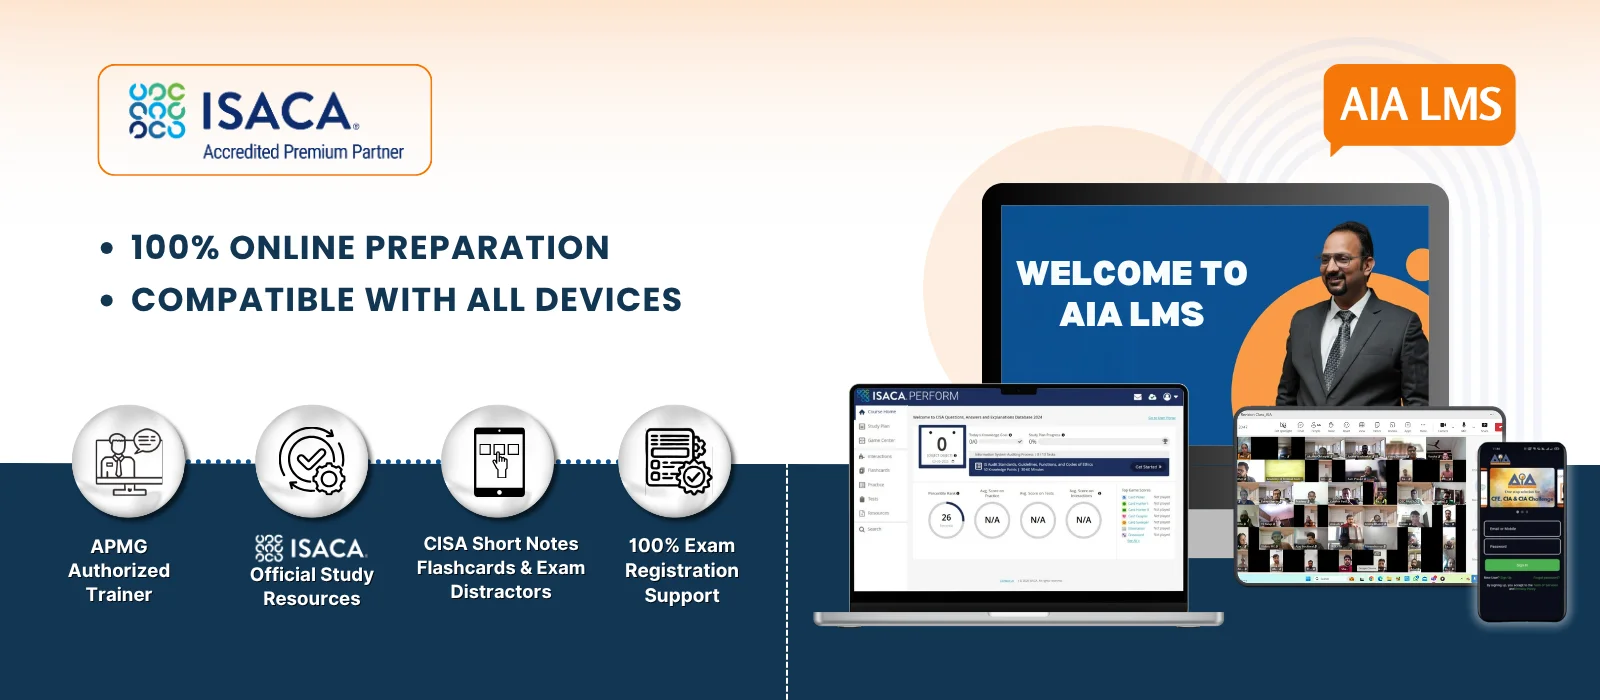
AIA’s LMS makes CISA prep simple and seamless - Study Notes, Video lectures, all in one place. Compatible with all devices. You’ll get full access to the AIA LMS for 6 months, so you can revise at your own pace.
Video Lectures
Online access to the recorded version of live classes will be provided to clear the concepts mentioned in the notes. Total recorded classes of more than 50 hrs will be provided, so you can view them at your own pace.
Instant Doubt Sessions
Got any doubt? Don't wait for the next class. Share your query directly with AIA's expert faculty on WhatsApp and get it resolved - quickly, clearly, and personally. Just real answers from real experts.
Examination Enrollment Support
AIA helps you with complete CISA exam registration support, including ISACA account guidance, exam scheduling assistance, and step-by-step support to make the registration process simple, smooth, and stress-free for aspirants.
Flashcards & Exam Distractors
With the AIA CISA Prep Course, you will get access to 400+ Flashcards & 500+ expert-created exam distractors designed to improve analytical thinking, strengthen decision-making, and prepare you for tricky CISA Exam scenarios.
Official CISA Prep Kit of ISACA
Prepare with official materials from ISACA. Get full access to the official prep kit and resources to ensure you are learning from the authoritative source.
Prepare with official materials from ISACA. Get full access to the official prep kit and resources to ensure you are learning from the authoritative source.
CISA Official Review Manual
You will get access to 500 pages of ISACA’s official CISA Review Manual covering all exam domains with structured concepts, updated content, and exam-focused explanations to support effective learning, revision, and preparation.
Why AIA is the Preferred Choice for CISA Prep
We provide a complete support system to ensure your success in CISA certification.
ISACA Authorised Training Organisation
AIA is officially recognised by ISACA to deliver CISA preparation. Every session, every resource, and every concept is aligned to ISACA's global exam standards, so you prepare with full confidence and authority.
ISACA Official Prep Kit
Get access to ISACA's official CISA practice exam and study guides. AIA provides the complete ISACA resources kit, including exclusive resources for CISA prep. Everything you need to prepare is in one place.
Structured & Exam-Aligned Curriculum
AIA's CISA prep follows a clear, domain-wise learning path built around what the CISA exam actually tests. Each concept is explained with a real-world IS audit context.
Expert-Led Teaching Methodology
Our preparation is led by Puneet Garg, APMG Authorised Trainer with deep expertise in IS audit and governance. Every session is designed to build exam readiness and professional judgement simultaneously.
Instant Doubt Solving Support with Faculty
AIA provide instant doubt-solving support where learners can actively address their queries on WhatsApp with faculty.
Mentorship & Enrolment Support
From CISA Exam registration guidance to final exam readiness, we support learners at every stage. At AIA, we simplify the ACFE enrolment process and ensure a smooth journey.
The Right Certification Starts With The Right Choice
Find the certification that aligns with your background and career stage
Find the certification that aligns with your background and career stage